Every finding,
turned into proof.
The compliance, reporting and management layer for NodeZero. Turn validated attack paths into clear priorities, evidence mapped to your compliance frameworks and reports for every audience.
 NodeZero evidence
 Microsoft
Sentinel
 Google
SecOps
One pentest.
Three conversations.
NodeZero shows how an attacker gets in. Your board, your auditors and your IT team each need a different answer from the same evidence — and NIS2 makes that answer a management responsibility.
From pentest to proof
in 90 seconds.
See how OpinioSec Portal turns NodeZero evidence into priorities, compliance evidence and reports for every audience.
 ▶ 1:27 · with sound
NodeZero at the core.
Your stack around it.
NodeZero evidence and scanner findings in one workflow for review, reporting and follow-up — with every event streamed to your SIEM.
 Microsoft
Sentinel
 Google
SecOps
Tenable / Nessus, Qualys VMDR and Rapid7 InsightVM via API or CSV · BlackstoneOne via CSV · Splunk HEC, Elasticsearch, Microsoft Sentinel, Google SecOps / Chronicle and Syslog / CEF out
Three signals.
One priority.
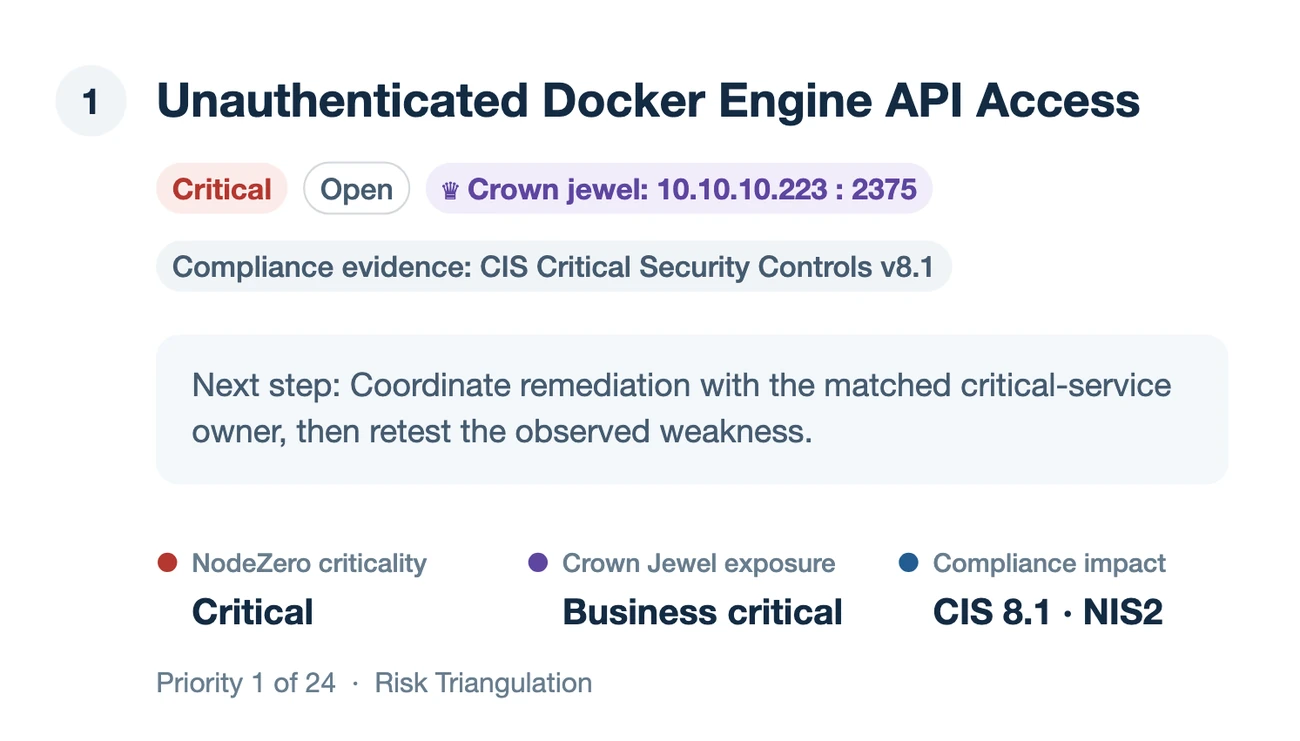
Combine technical criticality, business importance and compliance impact — so the next thing to fix is the one that matters most.
150+ compliance frameworks.
One body of evidence.
Choose the compliance frameworks you answer to. OpinioSec Portal maps the technical evidence NodeZero already found to the controls behind them — and keeps scope and open issues visible.
Mapping evidence to compliance frameworks supports your compliance work; it does not by itself establish compliance.
12 standard reports.
Every audience.
Choose the audience, evidence source and reporting period — then share as PDF or Excel, by email or webhook. Source, observation time and finding status stay visible next to every number.
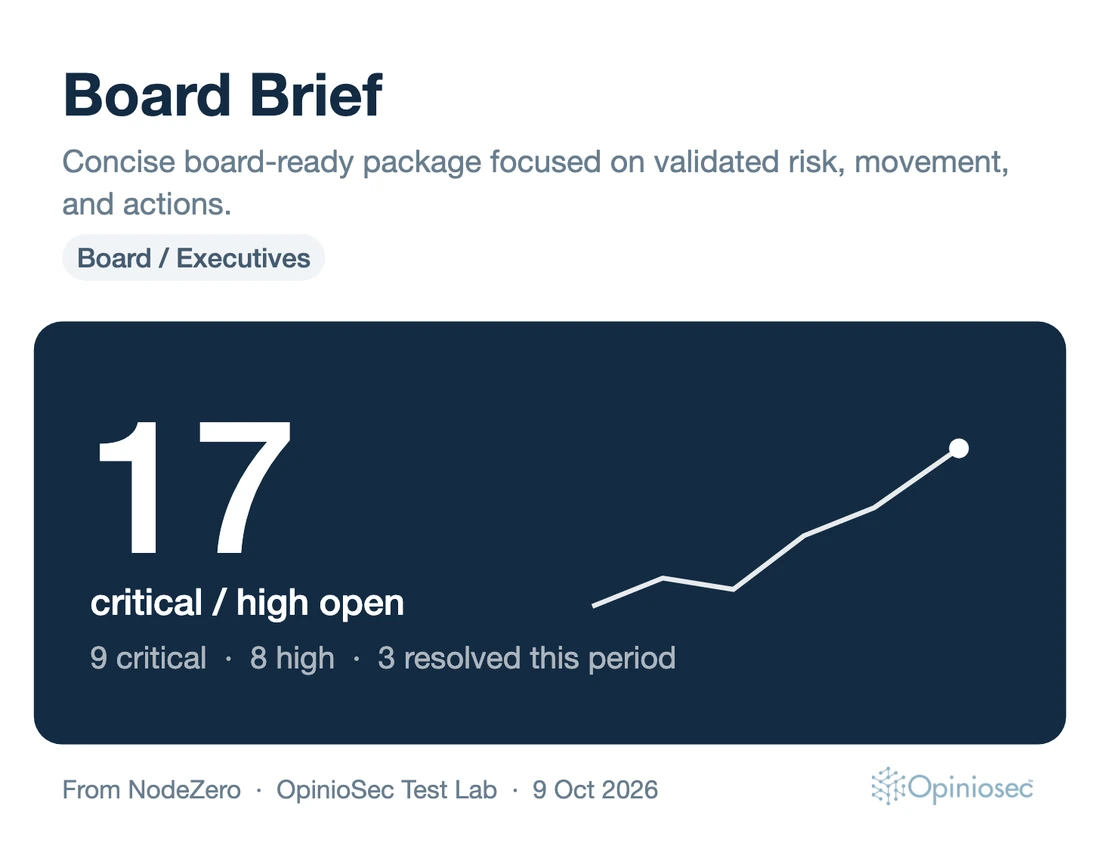
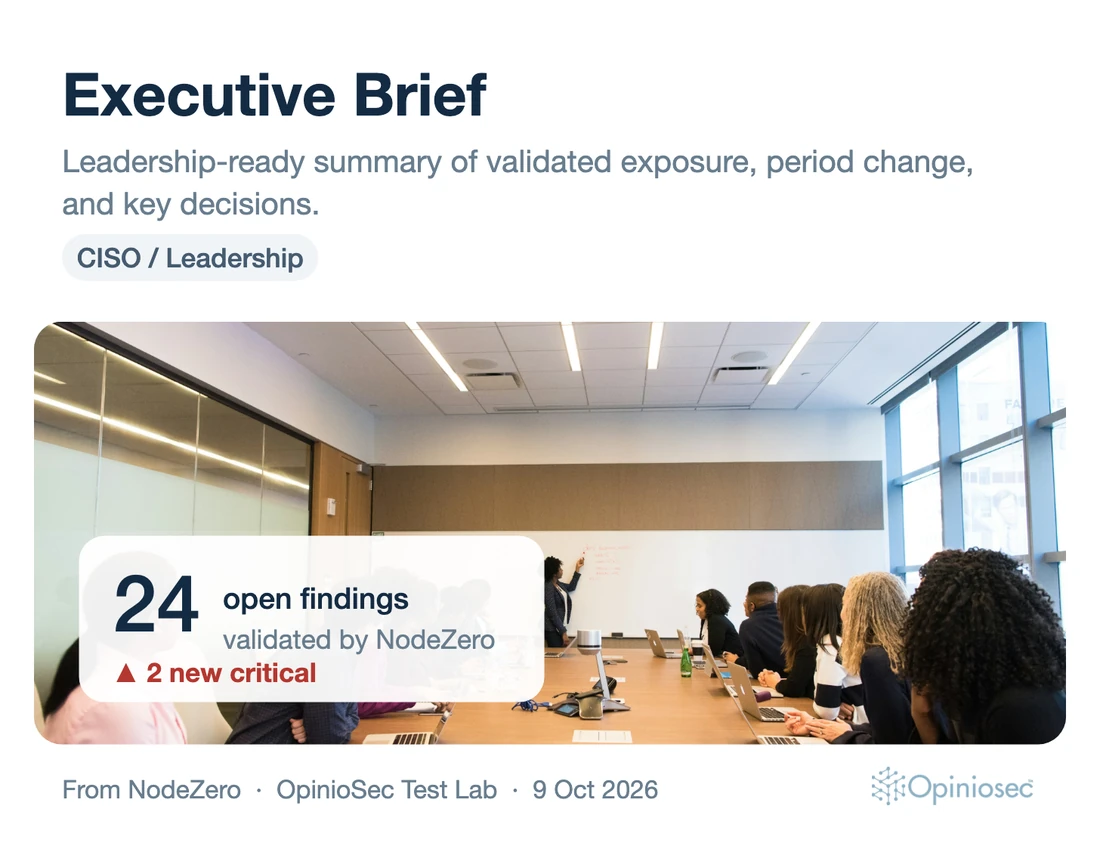
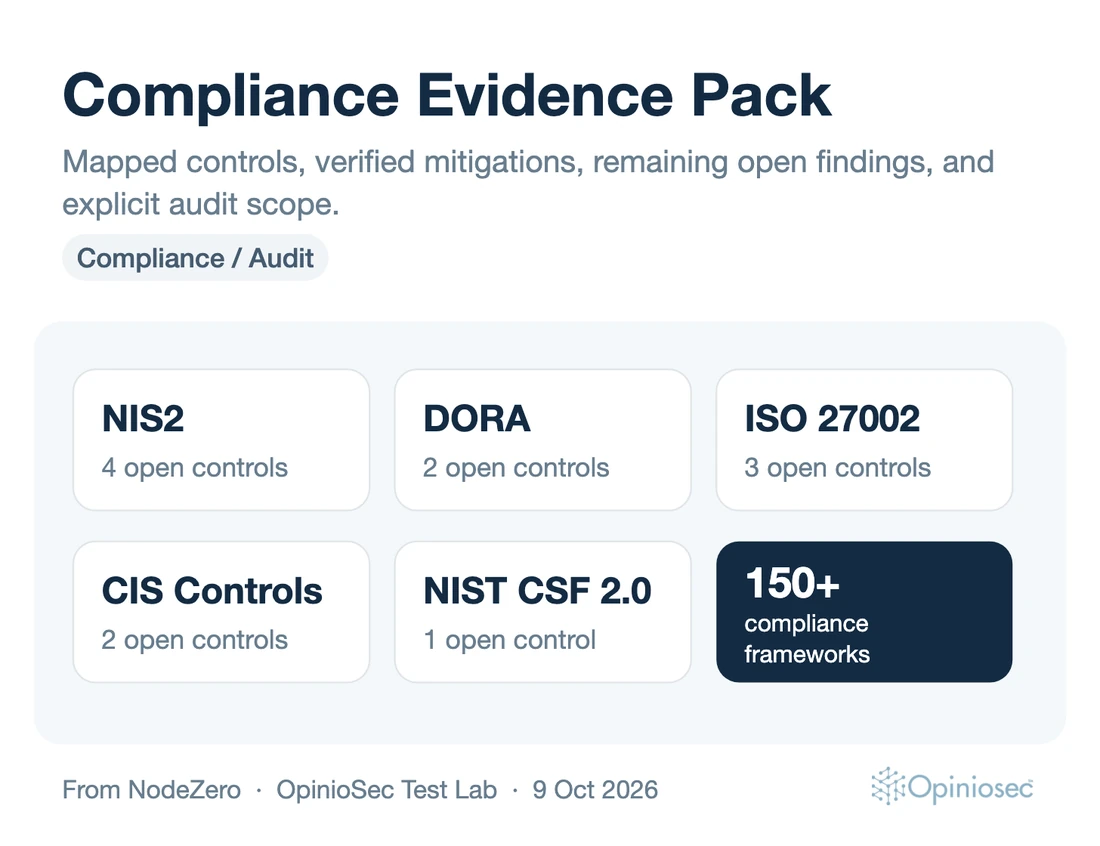
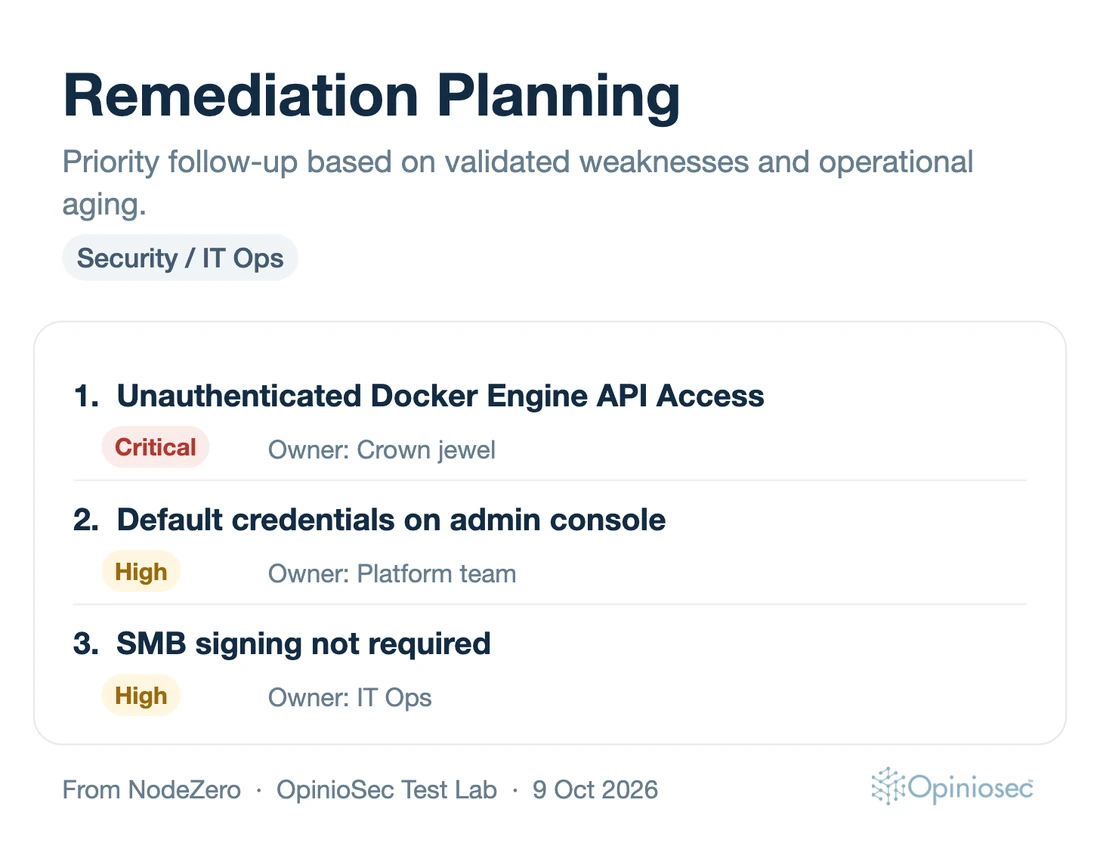
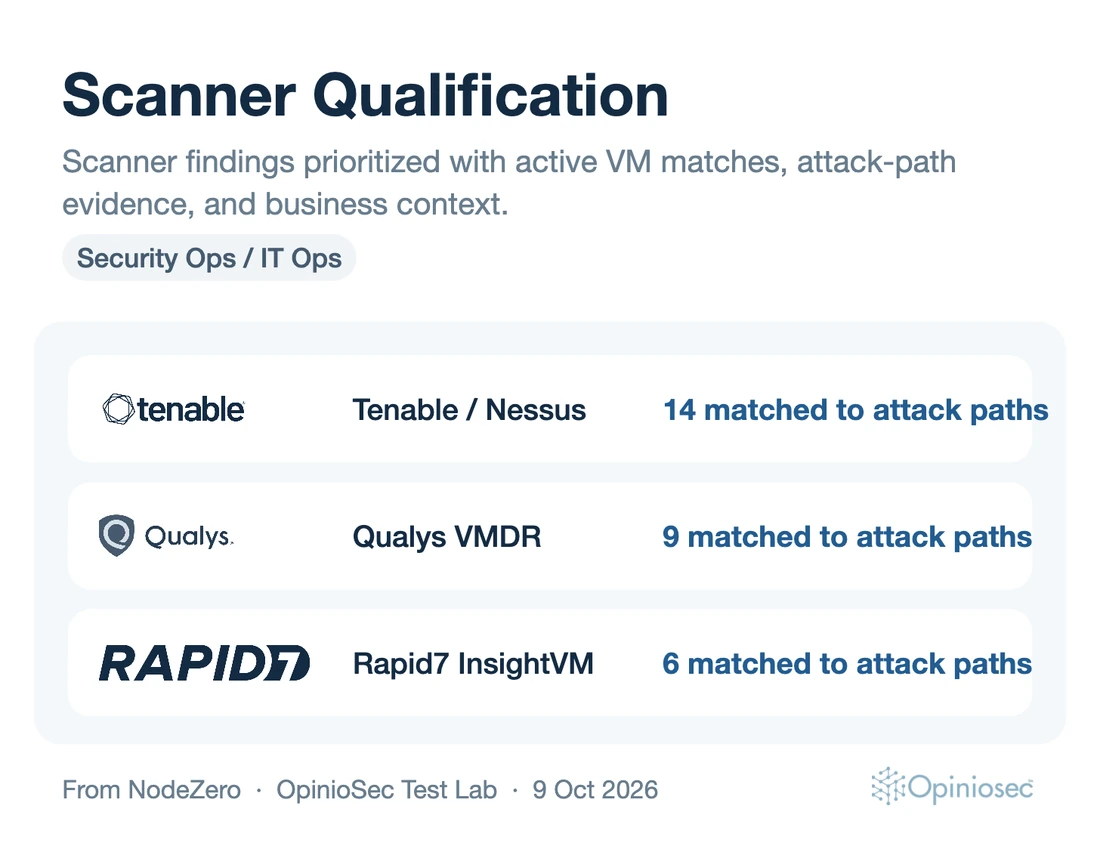
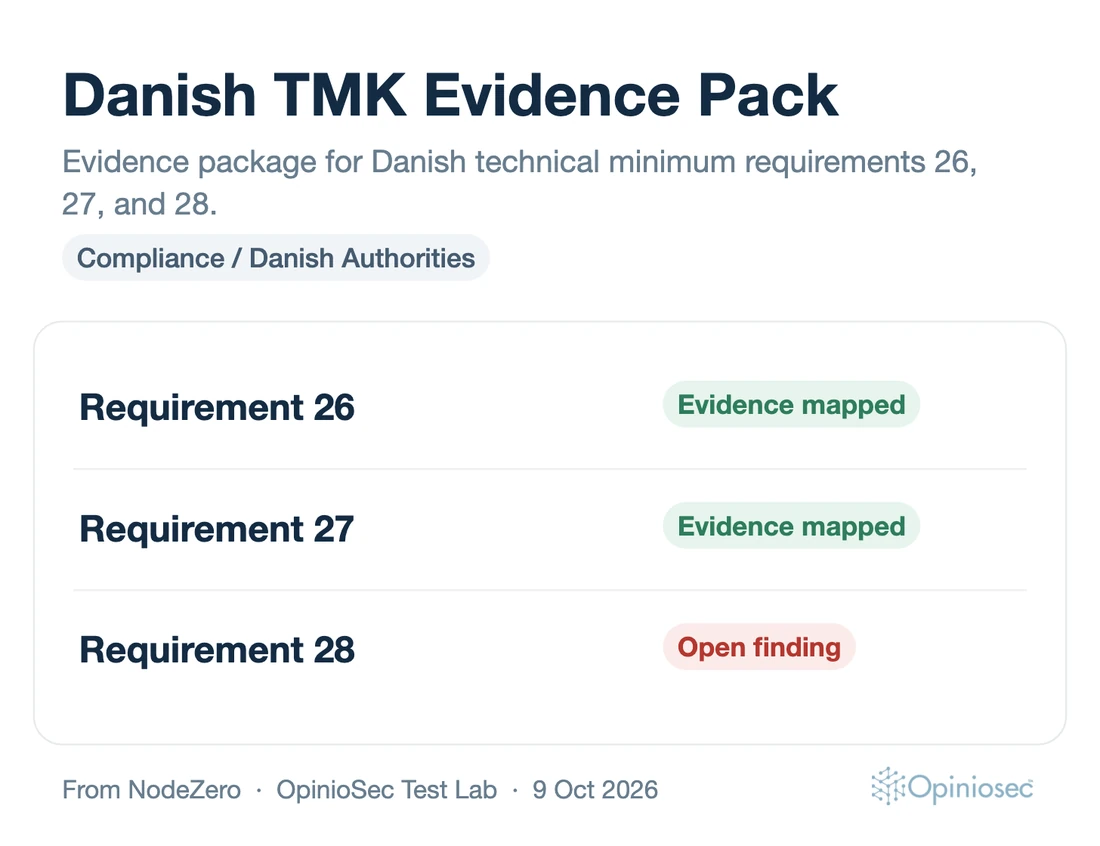
Board Brief · Executive Brief · Compliance Evidence Pack · Remediation Planning · Scanner Qualification · Danish TMK Evidence Pack — and six more standard reports.
Turn one test into
an ongoing review process.
Crown Jewels
Mark the assets the business depends on. Criticality and ownership flow into your NodeZero priorities and reports.
Scanner Qualification
Match Tenable, Qualys, Rapid7 and BlackstoneOne findings to NodeZero attack paths — with evidence and business context.
Automation
When a pentest completes, evidence changes or a report is due: generate, notify or deliver — automatically.
Calendar & blackout windows
Recurring runs, blackout windows and iCal subscriptions for Outlook, Google Calendar and Apple Calendar.
Enterprise controls
Microsoft SSO, user roles, IP allowlists, time-limited support access and a complete audit log.
Data administration
Configurable retention, privacy export and reusable report distribution lists.
See it on
your evidence.
A demo built around your priorities — your NodeZero data, your compliance frameworks, your audiences.
- Your NodeZero findings, prioritised with Crown Jewels and Risk Triangulation
- Your compliance frameworks — NIS2, DORA, ISO 27002 and more — mapped to the evidence
- The reports your board, auditors and IT team actually need